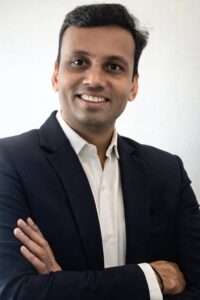
Vikas Somani, Vice President, Sales, India, at Eventus Security, speaks about managed security demand, partner opportunities, incident response readiness and the effect of AI on security operations.
Why are more enterprises in India choosing managed security over building their own SOC?
Building a SOC is the easy part. Running it well every day is harder. The real challenge is finding skilled people, keeping them, covering every hour and keeping pace with changing threats.
That is why managed security is gaining ground in India. Enterprises get specialist expertise and round-the-clock monitoring without building everything in-house. Costs also become more predictable once you count hiring, training, technology and upgrades.
For a CTO or CISO, the decision is about using resources wisely while keeping security at the right level.
No single model suits everyone. Some organisations need a fully managed SOC. Others have an internal team and need help strengthening it. At Eventus, we start with the customer’s needs and build a model that fits the business, not just more technology or people.
Which services are seeing the strongest demand right now: SOC-as-a-Service, Managed XDR, incident response, or cloud security?
Demand is strong for SOCaaS and Managed XDR. Enterprises want constant visibility into threats and fast response. Cloud security matters more as workloads move to the cloud. Incident response stays critical, both for preparing for an attack and for managing one.
These services are not rivals. They cover different parts of the same challenge, and customers increasingly want them together.
Starting points differ. Some need 24×7 monitoring. Others want to improve an existing SOC, or need clearer visibility across cloud environments. We find the gaps and build from there. The conversation is shifting from buying separate tools to building a security operation that detects threats early, responds well and helps the business recover.
How do cybersecurity priorities differ between India, the Middle East, and Southeast Asia, and how does Eventus adapt its partner approach?
The core concern is the same in all three regions: protecting the business, keeping customer trust and keeping operations running through an incident. The differences lie in customer expectations, budgets, regulations and how services are delivered.
India is diverse. Large enterprises may want advanced capabilities. Many mid-sized firms need expertise they cannot easily build themselves. Regional partners play an important role in reaching them and understanding their needs.
In the Middle East, local regulations, data-handling rules, procurement processes and service expectations shape how we approach a customer.
Southeast Asia is just as varied, with different requirements by country and industry, especially for organisations operating across several markets.
No single approach works everywhere. Our partner strategy combines our technical and service delivery strengths with the partner’s local knowledge and customer relationships. A strong partnership is about more than winning business. It means understanding the customer, setting the right expectations and delivering a service that lasts.
What is the biggest mistake enterprises make when outsourcing security? How can Eventus or their partners help them avoid it?
The biggest mistake is assuming that outsourcing security also outsources responsibility. It does not.
A provider may spot a compromised account or an active attack. Someone on the customer’s side may still need to approve the response. Can the account be disabled at once? Can a critical system be isolated? Who decides, and how fast? If this is not agreed in advance, even a good team loses time.
That is why the talk before signing matters. Customers need clarity on scope, escalation steps, decision authority and what each side must do. They also need a clear way to check that the service delivers the intended results.
At Eventus, we set these expectations with customers and partners at the solution design stage. What is promised commercially must be backed by a workable operating model. Outsourcing works when both sides understand their roles and act as one team.
Where do you see the partner-led cybersecurity market heading over the next one year?
Over the next year, more partners will move beyond selling security products. They will build ongoing services around their existing customer relationships. Technology sales are often the starting point, but customers need continuing support as their IT environments, business needs and threat exposure change.
That opens a chance for partners to earn recurring revenue and become more relevant. Managed SOC, Managed XDR and cyber resilience will be central to that conversation. Partners need not build every capability. They can work with specialised providers.
Customers will also want proof of value. Beyond the technology deployed, they will ask whether threats are detected faster, incidents are handled well and security posture is improving.
At Eventus, we want deeper relationships with partners who want a sustainable cybersecurity business, not one-off deals. Partners that combine strong customer relationships, the right technical capability and consistent delivery will be well placed to grow.
How can a partner with no security team of its own start offering services like threat intelligence, forensics, or GRC through Eventus?
A partner does not need a security team to enter this market. It needs a strong customer relationship, an understanding of the customer’s business and the ability to spot where specialist help is needed.
The partner can identify a requirement and bring Eventus in early. Our specialists assess the situation, recommend the right service and define how to deliver it. The partner avoids heavy upfront investment in a security operation.
A customer may need threat intelligence to understand risks to its business, or GRC support to strengthen governance and prepare for audits. Forensics is more specialised, as it demands technical expertise and careful evidence handling. In each case, the partner stays the customer’s main contact while Eventus supplies the expertise and delivery.
Over time, we also help partners build their own knowledge through training, joint customer engagements and solution development. The aim is a practical way into cybersecurity and, gradually, a more substantial security business.
What makes the Eventus partner programme different, and how do training, pre-sales and solution design support help partners sell specialised services with confidence?
A partner programme is not just about appointing partners and handing them a service catalogue. It is about building a sustainable business together and making sure customers get the right solution and the service they expect.
Cybersecurity can be hard to enter, especially when services need specialist skills. So our support goes beyond product training. We help partners understand customer requirements, find the right opportunities and bring in our technical teams when needed.
Pre-sales support helps meet the requirements. Solution design gives the proposed service a clear scope and ensures it can be delivered well. We also offer joint marketing, deal registration, dedicated account management and involvement during implementation and ongoing delivery.
Partners can then focus on customer relationships, knowing the right expertise is available. A programme succeeds when both sides own the customer relationship and the commitments made. For us, the measure is not only the business we win together, but the quality of service and the trust built over time.
Why do so many incident response plans fail when a real attack happens, and what separates organisations that recover quickly?
Often the plan exists on paper but has never been tested in a realistic situation. When an attack hits, people may know the process but not who must make which decision, or how fast.
A cyber incident is not only a technical problem. The security team may need to isolate a system at once, while business leaders weigh the impact on operations, customers and critical services. If decision authority is unclear or the right people cannot be reached, time is lost.
Organisations that recover faster prepare ahead. They run realistic simulations, involve business leadership, review backup and recovery arrangements and make sure internal teams can work well with external incident response specialists.
Recovery should not be rushed either. Teams must check that the threat is contained and the underlying vulnerability fixed before normal operations resume.
Readiness cannot be measured by a document alone. It comes down to whether people know their roles, decisions come quickly and the organisation can restore operations safely.
How is AI changing what customers expect from a managed security provider?
AI is changing expectations significantly. Customers now expect faster investigations, better use of available information and less time spent on repetitive tasks. They also expect their security tools to work together instead of in silos.
But customers do not want AI for its own sake. They care whether it spots a serious threat earlier, shortens investigations and gives a clearer picture of risk.
At Eventus, we see AI and automation as a key part of how security operations have evolved and will keep evolving. AI can help analysts work faster and focus on threats that need human judgement. Technology alone is not enough, though. It needs the right processes, expertise and accountability.
Customers will also want clarity on how AI is used, which actions are automated and where humans step in. The real measure is the improvement customers see in their security, not how much AI a provider claims to use.
If every enterprise had a fully autonomous SOC by 2030, what would still make a trusted partner indispensable?
Even with a fully autonomous SOC, enterprises must still decide what they are protecting, which risks they accept and how security decisions fit their business priorities. Technology can detect a threat and suggest a response. Understanding the wider business impact still takes context and judgement.
Isolating a system may be the right security call, for example. But what if that system supports a critical business operation? These decisions need an understanding of the business as much as the technology.
Businesses also keep changing. They adopt new technologies, enter new markets and shift how they operate. Their security needs change too, and someone must keep the strategy in step.
Automation will change the role of a trusted partner, not remove it. There may be less manual monitoring, but the need for sound advice, independent assessment and accountability will remain.
Customers will not value a partner just for its technology. They will value one that understands their business, tells them what they need to hear and stands by them when the stakes are high.