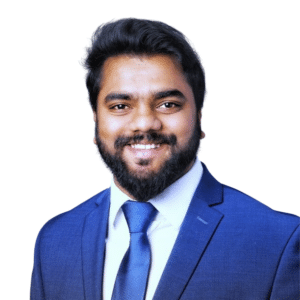
Setu Parimi is Co-Founder and CTO of RiskProfiler. In this interaction, he elaborates upon how agentic AI is changing threat investigation and how his team keeps AI findings trustworthy. He also covers how attackers use AI, and which industry is hardest to protect.
You co-founded RiskProfiler in 2023. What gap did you see in the security market?
Security teams have no shortage of alerts. They lack the context to know which threats matter and how separate risks can combine into an attack.
A leaked credential shows up in one tool. A lookalike domain shows up in another. A compromised vendor and an exposed cloud asset sit in two more. Each tool finds a real risk. None connects the dots or explains the business impact. Teams are left to piece together fragments and rank thousands of findings.
Our experience in cybersecurity leadership, penetration testing, cloud security and third-party risk showed us the disconnect. The industry is organized around product categories. Attackers work across them. They do not separate brand protection from dark web intelligence, attack surface management or supply chain risk. They combine small exposures into real attack paths.
We co-founded RiskProfiler in 2023 to build one intelligence-driven platform. It sees an organization’s external ecosystem through an attacker’s eyes. It links assets, identities, executives, brands, vendors and emerging threats into one view of risk.
Today, we are going further with agentic AI. Specialised agents find exposures, correlate threats, spot attack paths and help teams fix what matters most to the business. We did not want to build another tool that creates more alerts. We wanted one that connects the dots and helps teams act before attackers do.
What does a CTO at a cybersecurity startup spend most of their time on, and how has that changed?
In year one, almost all my time went into building.
I wrote code, designed the data pipeline and the knowledge graph beneath it, and sat with early customers to learn which alerts they acted on.
Today my time splits three ways. First is the architecture of KnyX. I stay close to how agents are scoped, what evidence they must collect and how verdicts are scored and logged. These choices are hard to reverse.
Second is customers and partners. I spend time with CISOs and with our MSSP and channel partners across India, Australia, New Zealand and the Middle East. Watching how a team triages gives the best product input. I still attend Black Hat and DEF CON. This year we ran one-to-one demos of the KnyX agents there.
Third is trust. That covers security reviews, SOC 2 and ISO 27001 evidence, and tough buyer questions about how AI touches their data.
The biggest change is that I now build the team and system that produce the answer, instead of writing it myself. The skill I use most is saying no. One agent that investigates reliably beats five that only demo well.
AI can produce confident but wrong answers. How do you validate KnyX’s findings?
The model does not decide what is true. The evidence does.
KnyX agents follow structured, deterministic steps, the same ones a senior analyst would take. For a lookalike domain, they check registration data, DNS, hosting and certificates, and whether a live phishing page is up. Each result is saved as evidence and must pass a schema check. The verdict is the conclusion of that evidence, with a confidence score. It is not the model’s opinion.
We also cross-check. A vendor-breach claim from one source is not treated as fact until other trusted sources back it up. Credential checks run only against domains we have verified the customer owns, and only through identity providers they have authorized.
Everything is reproducible. Each investigation records its inputs, outputs, evidence, execution history and the versions of the agents and skills used. If an analyst disagrees with a verdict, they can see how it was reached. Trust in a security tool does not come from never being wrong. It comes from being checkable.
You recently launched an MCP Connector for AI assistants. Why does it matter?
Most security teams have the data. They lack the time to find it. An analyst studying one domain may open five modules, filter each and stitch the answer together in their head.
With the MCP Connector, they can ask what RiskProfiler knows about a domain. They get exposure, digital threat, credential and vendor context in one answer, then keep asking follow-ups. A CISO can ask for a morning briefing on what changed overnight across the attack surface, vendors, brand and identities.
Two design choices matter. RiskProfiler stays the system of record. The assistant sees only what that user is already allowed to see. The connector is an interface, not a new home for data. We launched with Claude. ChatGPT and Gemini are planned.
In the next few years, I expect the assistant to become the front door to security tools. Analysts will start with a question, not a dashboard. Dashboards will become the place to verify. Vendors will win if their data is trustworthy enough to query in plain language, with permissions that hold. The assistant helps a qualified person move faster. It does not replace their judgment.
How are attackers using AI, and how does that change your defences?
The biggest shift is cost. Reconnaissance, phishing kits, lookalike sites and credential testing once took a skilled person’s time. AI makes each one cheap and fast. Convincing fake sites go up in minutes. Phishing copy reads cleanly in any language. Credentials from stealer logs get tested at scale.
Last month, Gambit Security published research on a campaign against online retailers that used a set of AI agents. Separate agents handled target selection, vulnerability discovery, intrusion and card skimming, at roughly $25 per target. When attacks cost that little, attackers can afford to try everyone.
This changes our defences in three ways. First, we automate the investigation, not just the detection. If attackers automate the attack, defenders cannot check every alert by hand. That is why we built KnyX Autonomous Investigations. Second, we measure the time from exposure to fix. We look for the one fix that breaks an attack path, instead of a longer alert list. Third, we treat AI as attack surface. Exposed model endpoints, AI APIs and data pipelines now appear in external scans. We monitor them like any other internet-facing asset.
How do you balance moving fast on AI features with commitments such as SOC 2 and ISO 27001?
I do not see it as a balance. Our compliance programme is what lets us move fast. When every AI feature goes through the same controls as the rest of the platform, we do not re-argue security each time we ship.
AI features are in scope from day one. Access control, change management, logging and vendor review apply to agents like any other part of the platform. Each agent gets the narrowest access its job needs. A credential investigation agent can touch only verified customer domains and the identity providers the customer has authorized.
Every agent and skill is versioned, and the version used goes into the audit trail. So we can trace any change in behaviour to a release. New interfaces inherit old permissions. The MCP Connector uses the platform’s existing permission model.
Where we slow down is actions. Reading and correlating data can ship quickly. Anything that changes something in a customer’s environment, such as resetting a password or filing a takedown, sits behind customer-defined policy and gets more review before release.
Many vendors now say they are “agentic.” What does that mean at RiskProfiler, and where do humans stay in the loop?
For us, agentic means the system does the investigation, not just the detection. A KnyX agent takes an alert and gathers the evidence an analyst would. It reaches a verdict with a confidence score and, where policy allows, acts. We call the loop Alert, Investigate, Verdict, Remediate. Today we have agents for leaked credentials, lookalike and typo squatted domains, live phishing pages, vendor-breach validation and threat intelligence filtering.
“Where policy allows” is the key phrase. For each remediation action, the customer decides whether it runs automatically, goes to a person for approval or stays off. Most teams start with approvals on, watch the agent work, then switch on automation one action at a time. A CISO at one of our retail customers told us it was the first time he could explain autonomous response to his board, because every action had a policy and an audit trail behind it.
Humans stay in the loop in three places. They set the policy, and no agent decides its own permissions. They approve actions that touch identities, customers or third parties, until they choose to automate them. And they review thin evidence. A low-confidence verdict is a question for an analyst, not an instruction to act.
Which industry is the most challenging to protect, and why?
From the outside in, retail. That surprises people, who expect me to say finance or healthcare.
Banks have large security teams and regulators who force investment. Healthcare is hard too, with legacy systems and medical devices that are hard to patch. Retail has a different problem. The brand itself is the attack surface. Every promotion, seasonal campaign and new market creates domains, landing pages, apps and social accounts. Attackers clone them within hours as fake stores, fake support lines and phishing pages. Customers cannot tell the difference, so the fraud lands on the brand.
Retailers also depend on third parties, such as payment providers, logistics firms, marketing agencies, franchisees and e-commerce plugins. Each is a way in. And the security team is often small next to the footprint it protects. The AI-driven attacks on online stores this year show where this is heading.
Is there a common misconception about external attack surface management?
The biggest is that EASM is an asset inventory. Teams buy it, get a list of every domain, IP and certificate they own, and think the job is done. Then the list has ten thousand rows and nobody knows where to start.
An inventory is a starting point, not the outcome. External risk is not a list of assets. It is the set of paths an attacker can actually walk. A forgotten staging server matters far more if someone’s credentials for it are in a stealer log and a vendor that was just breached hosts it. Alone, each is a medium finding. Together, they are an incident waiting to happen.
The second misconception follows: that your attack surface is only what you own. Your vendors’ exposures, your executives’ leaked credentials and the lookalike domains imitating you are all part of it. None of them sits in your asset register. Good EASM connects all of it and shows which single fix breaks the path.